Data Protection

Your files stay on your devices and travel directly between them. Gavety is designed so that we never receive or read your file contents.

Layers of protection

Privacy built into every layer

End-to-End Encryption

File transfers between your devices are encrypted in transit with WebRTC. Encryption keys are negotiated between your devices for each session.

No Central File Storage

Our servers never store your files; they hold only account, device and licence records. Your data lives on your physical drives at home — no single point of failure.

Encrypted Handshakes

Our signaling servers facilitate connections via TLS 1.3, ensuring even the “directions” to your server stay private. See how global access is structured.

Why it’s different

Your privacy is hard-wired, not promised

Traditional cloud storage keeps your files on the provider’s servers. Gavety is designed so your files never reach ours.

By using peer-to-peer tunneling, we eliminate the middleman entirely. Your fees fund software updates and the connection infrastructure that sets up these tunnels. Learn more about how the P2P connection works or get started with setup.
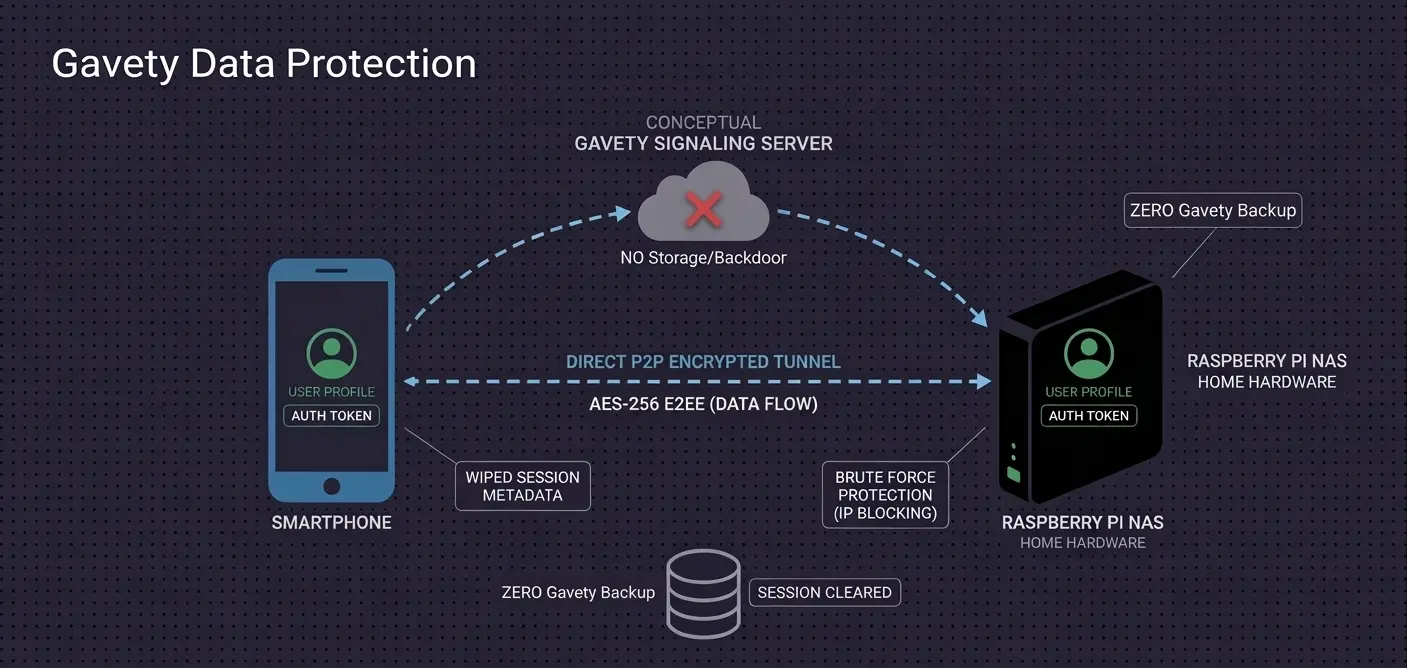
Gavety Data Flow
E2EE (Device-to-Device)Transfers between your devices are encrypted in transit (WebRTC). Keys are negotiated between your devices for each session.
Industry-Standard EncryptionConnections use WebRTC and TLS, the encryption standards used across the modern web.
Session Data HandlingConnection setup data is discarded when a session ends. Server logs are kept for up to 180 days, as described in our Privacy Policy.
Brute Force ProtectionAutomatic IP blocking prevents automated attacks on your local server.
TLS 1.3 HandshakeAll connection signals use the latest secure standard, ensuring private negotiation of P2P tunnels.
No Central File StorageYour files are not kept in a central repository for attackers to target. They stay on your own drives.
Promises vs. Design

Why “we promise” isn’t enough

Where your files live matters.

Typical Cloud Storage

  • Provider may hold copies of your encryption keys
  • Data stored on shared corporate servers
  • Provider can be compelled to hand over your files
  • A breach of the provider can expose many users’ files
  • Privacy depends on the provider’s policies

Gavety

  • Keys negotiated between your devices for each session
  • Data stays on your physical drives at home
  • Designed so Gavety never receives your file contents
  • No central file storage to breach
  • Privacy is built into the design, not just promised

Explore more about Gavety

From the blog

Ready for real privacy?

Set up your private cloud in minutes. No surveillance, no compromises.

Get started